
During Development
- Security Consultation
- Kann AI Scan
Kann Audits is a Web3 security audit company helping DeFi protocols, blockchain networks, and infrastructure teams build securely at every stage, from development to launch and beyond.
Trusted by teams building critical onchain systems
 Arche
 castr.fun
 APTree
 HyperLend
 Encifher
 Wild Protocol
 Manifest Finance
 Pulse In Private
 FactcheckDotFun
 Mystic Finance
 Gluon
Solutions for all
Kann Audits connects development, audit, and post-launch protection through a single integrated system. Each component plays a defined role in the lifecycle while remaining powerful on its own.
Our solutions
Choose a focused service or build a complete security program around your release.
Human-led smart contract security audits assembled around the architecture, business logic, integrations, and risk profile of complex Web3 protocols.
Explore Expert Security AuditsKann AI / Model Alpha extracts Solidity call graphs and returns function-level security signals for expert validation. It is an early analysis tool, not an audit certificate.
Explore AI Security ScanDefine security properties for critical protocol behavior and evaluate whether the scoped implementation satisfies those specifications.
Explore Formal VerificationA direct triage path for suspected exploits, critical vulnerabilities, suspicious transactions, and urgent remediation review. Availability is confirmed during triage.
Explore Incident ResponseExpert Security Audits
Kann Audits structures each manual review around the architecture and risk in scope. Researchers challenge independent attack paths, validate issues together, and stay engaged through fix review.
Explore Smart Contract Security AuditsKann AI / Model Alpha
Model Alpha extracts call-graph context and returns function-level signals. The interface makes candidate issues visible while keeping the most important step explicit: qualified human validation.
Explore AI Security ScanFormal Verification
Define the behaviors that must hold, connect them to the scoped system model, and investigate failed properties or counterexamples with their assumptions intact.
Explore Formal VerificationIncident Response
Preserve evidence, trace the affected path, evaluate containment, and review remediation without turning an urgent technical event into another uncontrolled risk.
Explore Incident ResponsePublished evidence
Real scopes, documented findings, remediation outcomes, and source PDFs from completed Kann Audits engagements.
HyperLend
May 26, 2026
HyperLend
castr.fun
August 13, 2026
castr.fun
Mystic Finance
May 11, 2026
Mystic Finance
Track record
Real results from real engagements, measured across audits completed, code reviewed, vulnerabilities found, and value secured.
How an audit works
Every stage narrows ambiguity, keeps evidence attached to the reviewed code, and gives remediation a clear place in the engagement.
Repository, commit, architecture, assumptions
Assets, trust boundaries, invariants
Manual adversarial review
Impact, evidence, severity
Developer response and fixes
Patch and regression verification
Scope, findings, final statuses
Insights, technical breakdowns, company updates, and perspectives on smart contract security, Web3, and AI.
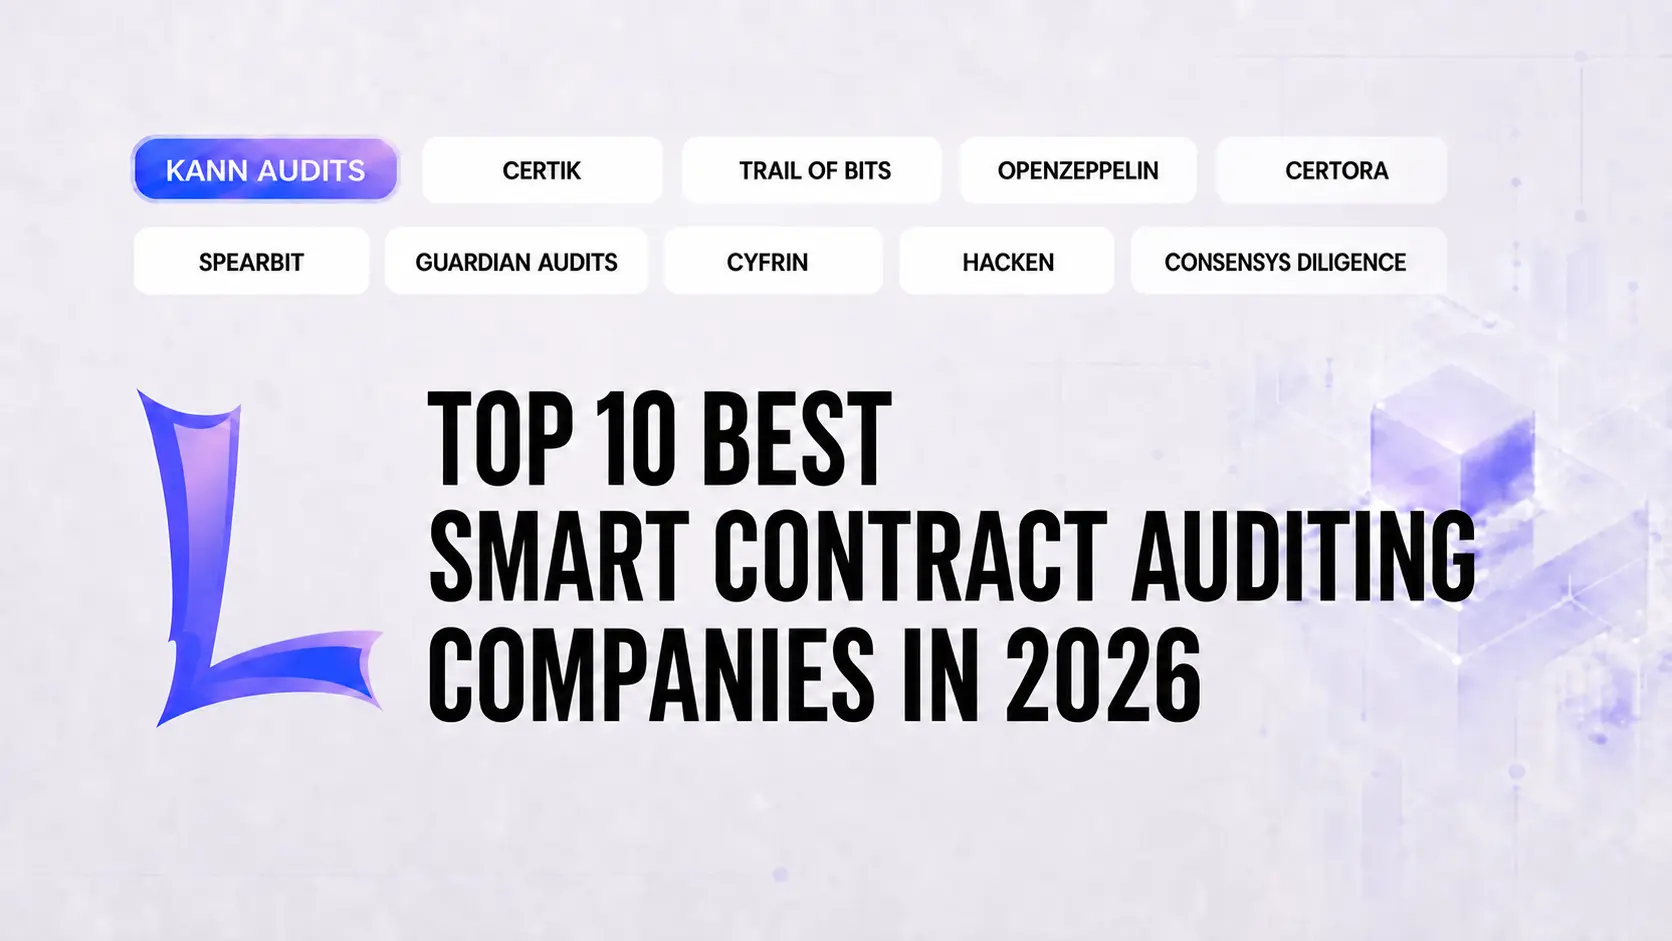
Billions of dollars continue to move through immutable smart contracts, while security incidents show that one overlooked assumption, compromised key, unsafe integration, or operational failure can create catastrophic loss. This evidence-led comparison examines ten leading audit providers, the models they use, and the situations each is best equipped to handle.
Read article
Robinhood Chain is EVM-compatible, but a credible review cannot stop at familiar Solidity checks. Its security surface extends into L2 operations, first-come-first-served sequencing, cross-chain messaging, Stock Token accounting, oracles, account abstraction, governance, and off-chain financial data.
Read article
Canton changes the unit of security analysis. Reviewers must reason about Daml workflows, selective visibility, participant infrastructure, and multi-application outcomes as one system.
Read article
Midnight expands the application security boundary across Compact contracts, private state, client-side proofs, TypeScript providers, wallets, indexers, and backend infrastructure.
Read article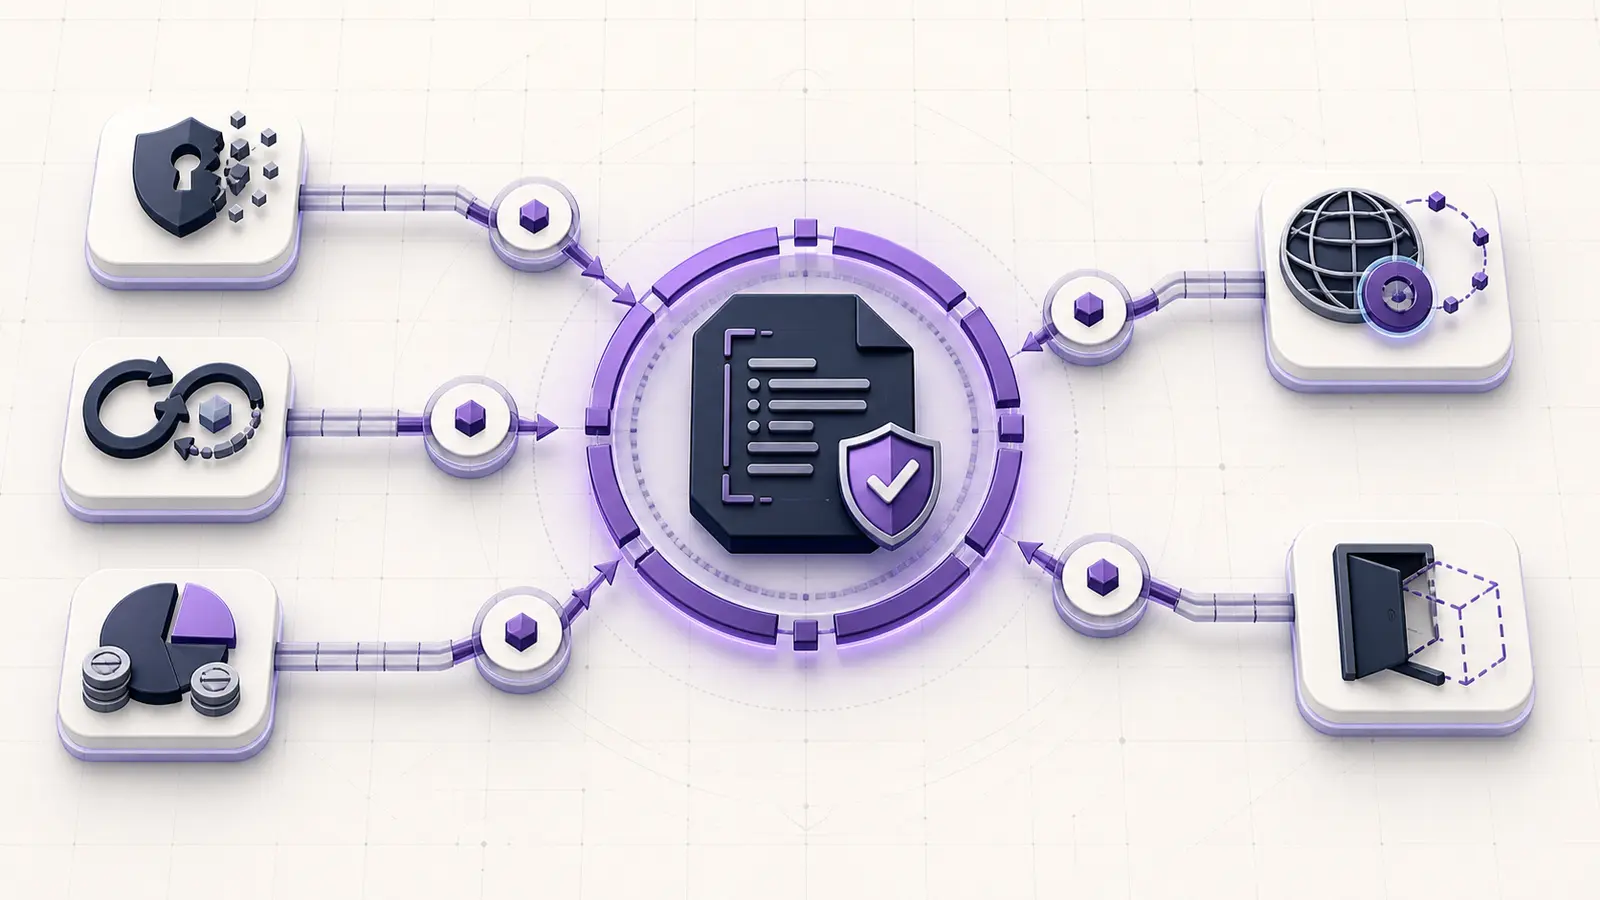
Major Web3 exploits often begin with a small mismatch between intended behavior and what the code actually permits. These five published findings show how cross-asset accounting, replay protection, reentrancy, share conversion, and state recording can become direct security boundaries.
Read articleFAQ
Kann Audits is a Web3 security company providing expert, human-led smart contract audits, formal verification, AI security scans, and incident response for protocols and blockchain infrastructure.
Kann Audits provides end-to-end security rather than a one-time code review. We combine expert-led security audits, formal verification, AI security analysis, and incident response to support protocols from development through launch and beyond, giving teams multiple security options through a single trusted provider.
Pricing depends on the programming language, nSLOC (net source lines of code), codebase complexity, and overall audit scope. We provide a tailored quote after reviewing the codebase.
Timing depends on scope, complexity, documentation, novelty, and researcher availability. The team proposes a schedule after reviewing the codebase and target date.
Our current capabilities include Solidity, Rust, Move, Go, DAML, zero-knowledge systems, protocol infrastructure, and off-chain components written in TypeScript and JavaScript. Final stack availability is confirmed during scoping.
A scoped review can include architecture, trust boundaries, access control, state transitions, accounting, integrations, adversarial research, validated findings, remediation, and fix verification.
Share a stable commit, architecture documentation, tests, deployment context, known assumptions, integrations, and a clear scope with enough time for remediation before launch.
Yes. Teams can work with researchers through remediation and fix verification so final statuses reflect the reviewed commit.
No. Each service is powerful on its own, and Kann Audits can also connect development, audit, and post-launch protection into one lifecycle model.
Kann Audits offers security consultation, AI Security Scan with Model Alpha, Expert Security Audits, formal verification, and incident response.
Kann Audits is built for protocols, institutions, infrastructure providers, L1s and L2s, bridges, DeFi platforms, wallets, and teams operating high-value onchain systems that demand rigorous security and technical assurance.
Start a conversation
Share the architecture, fixed scope, and target date. Kann Audits will help define the security work that fits the release.
RESEARCHER COMMENTValidate state ordering before the external asset transfer.